Physical Address
304 North Cardinal St.
Dorchester Center, MA 02124
Physical Address
304 North Cardinal St.
Dorchester Center, MA 02124
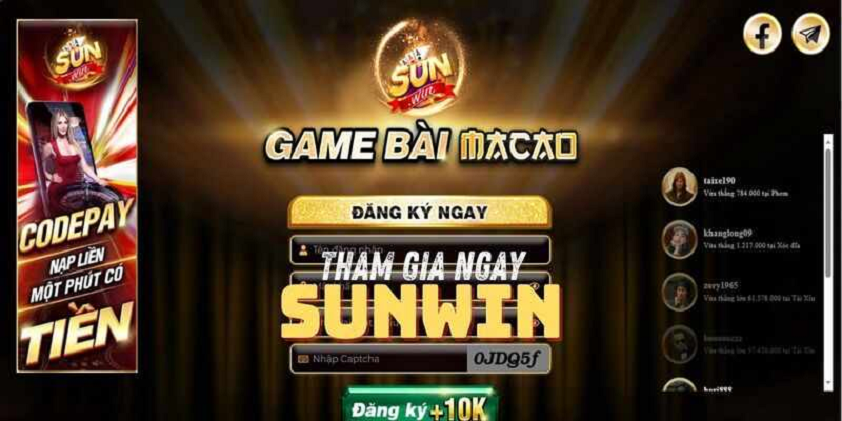
Imitation websites are designed to benefit from familiarity. They may reproduce logos, colors, page layouts, buttons, and even complete sections of text from another website. Some exist primarily to attract search traffic, while more dangerous versions attempt to collect passwords, personal information, payment details, or software downloads. Recognizing these pages requires users to look beyond visual appearance.
When researching sunwin, pay attention to the actual domain behind each result. A familiar name in a search title or page heading does not prove ownership or authenticity. Search engines may display official resources, informational guides, advertisements, community pages, and unrelated domains together, making source verification an essential first step.
The same principle applies to links received through social media, messaging applications, email, and online forums. A link should be evaluated according to its destination rather than the person or message that supplied it.
Look-alike domains frequently use minor spelling changes.
An attacker might replace a letter with a similar character, add a hyphen, insert another word, or choose a different domain extension.
On mobile devices, expand the browser address bar so you can see as much of the address as possible.
Do not rely on page titles alone.
Long URLs can make an unrelated site appear connected to a familiar brand.
The important part is the registered domain, not merely a recognizable word somewhere in the address.
Learning how domain structures work makes it easier to detect these tricks.
A logo is not an authentication mechanism.
Images can be copied within seconds. So can navigation menus, login forms, icons, fonts, and promotional banners.
Instead of asking whether the page looks familiar, ask whether its domain, security behavior, account procedures, and support information are consistent with independently verified sources.
Some imitation pages contain obvious mistakes.
Potential warning signs include broken navigation, inconsistent fonts, missing pages, unusual translations, spelling errors, placeholder text, and buttons that lead to unexpected destinations.
However, absence of these problems does not prove legitimacy. Sophisticated phishing pages can look extremely polished.
A website’s requests can reveal more than its design.
Be cautious if a login page unexpectedly requests extensive identity information, card PINs, banking passwords, recovery codes, or unrelated verification details.
The requested information should make sense for the action being performed.
Fake pages frequently pressure visitors to act immediately.
They may claim that an account will close within minutes, that verification must happen instantly, or that a special opportunity is about to disappear.
Urgency is a reason to verify more carefully.
Leave the page and independently check whether the same notification exists through a trusted route.
Do not download files simply because a page looks legitimate.
Applications and installation packages can contain malicious software.
Check the publisher and source, and take operating-system security warnings seriously.
Avoid instructions that require disabling antivirus software or other protections without a clear, legitimate reason.
Imitation websites sometimes provide fake support channels.
Search for consistency between contact information across sources. Be cautious when a page offers only a messaging account and immediately requests sensitive information.
Never send a complete password to customer support.
Users looking for information about đăng nhập Sunwin should distinguish between reading login instructions and actually submitting credentials. Before authentication, verify the destination independently and confirm that the page is appropriate for account access.
If a password manager normally fills your credentials but unexpectedly does not recognize a familiar-looking page, check the domain carefully.
The page may be located on a different address.
A unique password limits damage if credentials are exposed.
Never use the same password for entertainment accounts and your primary email.
Password managers make unique credentials easier to maintain.
Enable additional authentication where available.
A sponsored search result can appear before ordinary results.
Prominent placement does not establish authenticity.
Check the destination domain before clicking advertisements that claim to provide login pages, updated links, downloads, or account recovery.
Fake social accounts can support fake websites.
Impersonators may copy logos and descriptions, then direct users toward phishing pages.
Do not assume that a profile is legitimate simply because it has followers or polished graphics.
Look for consistent cross-references from independently verified sources.
Testimonials can be fabricated.
A page containing dozens of positive comments is not automatically trustworthy.
Look for evidence that can be independently evaluated: domain history, transparent policies, consistent support information, clear security procedures, and reputable external references.
Modern browsers can identify some suspicious websites.
If a browser displays a phishing, malware, or certificate warning, do not bypass it automatically.
Investigate the reason for the warning.
Security protections are particularly important when you are already uncertain about the page.
Simply viewing a suspicious page does not necessarily mean an account is compromised.
Risk increases if you entered credentials, downloaded files, installed software, or provided personal information.
If you submitted a password, change it immediately through a verified destination.
Change reused passwords elsewhere as well.
Do not continue opening suspicious files.
Use your device’s security tools to scan the file or system and remove questionable applications.
Review recently granted permissions.
If you provided administrative or accessibility permissions to an unknown application, revoke them.
If card or banking information was entered on a suspected phishing page, contact the financial provider using a verified phone number or official application.
Review recent activity and follow the provider’s instructions.
Do not use contact information supplied by the suspicious page itself.
Before trusting a page:
Imitation pages succeed when users recognize a brand faster than they examine the destination.
The solution is not to memorize every possible fake address. Instead, develop a repeatable verification process that works across websites.
Read domains carefully, question unexpected requests, protect credentials, verify support contacts, and avoid unknown downloads.
Visual familiarity can be manufactured. Consistent verification provides much stronger protection.